When a Big Four firm like Ernst & Young (EY) publishes a cybersecurity report, the business world and academia tend to take it at face value. But when GPTZero decided to check every citation in one such report, it uncovered a startling truth: much of the content had been generated by AI, and many of the citations were fabricated sources that do not exist.
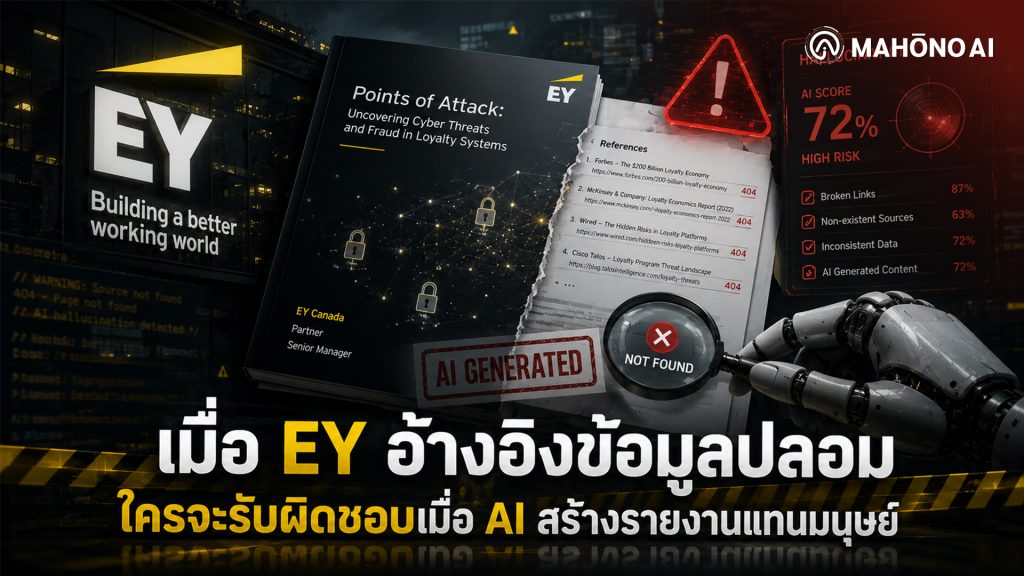
In late 2025, EY Canada published a 44-page cybersecurity report titled Points of Attack: Uncovering Cyber Threats and Fraud in Loyalty Systems. The report focused on cyber threats and fraud in loyalty and rewards programs, and it listed a Partner and a Senior Manager at the firm as its authors.
GPTZero’s investigative team ran every citation in the report through its Hallucination Check tool. They found that almost all of the URLs in the reference table were broken or had never existed, and that more than half of the cited sources did not match any real document. Clear examples include:
- A Forbes article titled “The $200 Billion Loyalty Economy,” cited with a broken URL. No such article exists.
- A McKinsey & Company “Loyalty Economics Report (2022),” which does not exist in McKinsey’s database. GPTZero traced this false citation to a blog post published just six months earlier by Financial IT, a small fintech magazine. That blog post cited the same fake source.
- Several Wired and Cisco Talos articles, all of which returned 404 errors.
Beyond the broken links, the report contains clear internal contradictions. The executive summary puts the global loyalty market at US$200 billion, yet on page 10 the same figure is used to describe only the value of unredeemed points. If that were true, the total market would have to be worth at least US$400 billion. Similarly, page 6 presents an 89% increase in attacks on loyalty programs without any time frame, while page 11 claims the figure applies only to 2018–2019.
A GPTZero scan gave the report’s text an AI score of 72%, indicating that most of the content was generated directly by AI.
The report’s impact was not limited to Canada. It was cited in a Canberra Times article that was syndicated to more than 60 newspapers across Australia. More worrying still, AI tools such as ChatGPT, Claude, and Perplexity all drew on this flawed report to answer user questions, spreading “toxic data” widely across the digital knowledge base.
The EY Canada case shows the real danger of a phenomenon known as “vibe citing”: citing AI-generated sources without checking that they are accurate. When a reputable institution such as a Big Four firm publishes false information online, that information becomes a source that AI systems reuse, which spreads the misinformation even further. GPTZero developed Hallucination Check to help detect this problem, and leading international academic conferences, including IJCAI, ICLR, and ICSE, now trust the tool to screen research submissions. In an era when AI can write reports, verifying sources is no longer optional. It is essential.
Source: GPTZero